

Antimalware Service Executable high CPU usually means Microsoft Defender is actively scanning, updating, or responding to files that changed. A brief rise is not automatically a fault. Before changing security settings, watch when the load appears and whether it falls after the task finishes. If the computer remains slow for hours or the same folder triggers the spike every day, investigate that pattern. Do not turn off real-time protection simply to make the graph look calmer; that removes a useful defense without finding the cause.
Confirm which process is busy and when
Open Task Manager with Ctrl+Shift+Esc and sort the Processes view by CPU. Look for Antimalware Service Executable, the Microsoft Defender process associated with MsMpEng.exe. Note whether the percentage rises only while you download files, open an archive, install software, or start a full scan. Let a short scheduled scan finish and watch whether the CPU use returns to normal. On a small laptop, a routine scan can feel heavy even when it is working as intended.
Do not judge from one frozen screenshot. Observe the process for several minutes while the computer is otherwise idle. Record the time, whether the system is on battery, and what else is running. An indexing job, a large update, or a game installation can compete for the same disk and make Defender appear to be the only culprit. If the high usage is continuous, write down the exact duration and any repeating trigger. That evidence helps you test a change instead of guessing.
If Task Manager shows a different process using the CPU, follow that process rather than applying Defender-specific advice. Also check whether the system is responsive enough to open Windows Security. A machine that overheats or shuts down under load may have a cooling problem alongside software activity. Security settings will not repair a fan or blocked vent. The goal is to distinguish ordinary scanning, a repeatable scanning conflict, and a broader hardware or software issue.
Check Defender’s own status before adjusting it
Open Windows Security from Start, select Virus & threat protection, and review current protection and recent scan information. If a scan is running, let it complete when practical. If updates are pending, use the protection-update option and Windows Update through their normal interfaces. Restart once after a completed update if Windows requests it. Then observe the CPU again under the same conditions. A resolved one-time update or scan needs no further intervention.
Microsoft’s Defender performance troubleshooting guidance recommends investigating what the scanner is doing instead of making broad exceptions without evidence. For a managed work PC, security policies may come from your organization. Ask IT before changing them. A home user should also avoid downloading a so-called optimizer that promises to stop the process; some such tools weaken protection or introduce new problems.
Check whether another security product is installed and actively scanning the same files. Do not assume that two icons mean two active antivirus engines; confirm each product’s state. If a second product is involved, consult its own instructions or the device administrator. Do not uninstall a security suite solely on a hunch, especially when it provides other functions. Make one controlled change at a time and compare CPU use afterward.
Find the workload that keeps triggering scans
A large folder changes repeatedly
Development builds, virtual machine images, and frequently rewritten archives can cause repeated file inspection. Watch whether CPU rises when that specific task runs and falls when it stops. If the pattern is reproducible, verify the folder’s purpose, owner, and trustworthiness. Excluding a location means Defender will inspect less of it. That is a security decision, not a generic performance tweak. Never exclude Downloads, an entire user profile, or a drive simply because it is convenient.
A scan remains busy on one file or path
Note the file path if a diagnostic tool or protection log makes it available. Do not open a suspicious file merely to test it. Large compressed files can take time to inspect, while corrupted or inaccessible storage may create repeated read attempts. Check whether the underlying drive remains connected and reports plausible capacity. If it clicks, disappears, or generates read errors, stop stressing it and protect data. Changing antivirus settings cannot fix damaged storage.
The slowdown appears during an installation or update
An installer often writes many files quickly. Defender may scan them as they arrive. Wait until the installation finishes, then measure again. If CPU stays high afterward, restart if the installer requires it and inspect Windows Security for an active scan or warning. Do not add a permanent exclusion for an unfamiliar installer. If it came from an unverified source, treat the security warning seriously and confirm the software publisher before running it again.
Make measured changes without losing protection
Start with low-risk steps: finish pending updates, allow the current scan to complete, and avoid running several disk-heavy jobs at once. A laptop on battery saver may feel different from the same machine plugged in; compare like with like. Keep Windows and Defender current through official controls. If the issue is limited to a known scheduled full scan, choose a time when the PC is normally idle using available organizational or product settings rather than disabling real-time checks.
Only consider a narrow exclusion after identifying a trusted workload and weighing the security cost. Specify the smallest appropriate path or process under the guidance for your environment. Document why you added it and test whether CPU actually improves. Revisit the exclusion later; a temporary build folder should not remain exempt forever. If you cannot clearly explain why a folder is safe to omit, leave it protected and seek qualified support.
Do not try to delete MsMpEng.exe, block security services, or follow a command that permanently disables Defender. Such actions may fail, weaken the PC, or be reversed by policy. They also hide the original performance evidence. If the machine is company-managed, an administrator may have diagnostic tools that identify scanned files and scan durations. Provide your recorded times and workload so they can investigate the specific trigger.
What if files disappeared while the PC was slow?
High CPU by itself is not proof that Defender deleted your documents. First check Windows Security’s protection history for a recorded action, then inspect the original folder, Recycle Bin, cloud versions, and backups. For an ordinary deletion, the Recycle Bin recovery steps may resolve the issue without scanning. If security software quarantined a file, follow its documented review process. Do not restore an item flagged as malicious merely because its name looks familiar; verify its source and consult IT when appropriate. This is a different problem from improving CPU performance.
Drecov is Windows data-recovery software, not a Defender tuning tool or malware remover. It becomes relevant only if a local file is genuinely missing from a stable, recognizable device and normal backups or version history do not supply it. Quick Scan can search the original location; Deep Scan broadens the search when the device stays stable. Filters and previews help locate supported documents, photos, and other files before restoring them to another healthy drive. Lost Partition Recovery is for a missing partition, not a high CPU reading. Drecov cannot repair hardware, reverse overwritten content, or declare a quarantined file safe. The file recovery overview applies only after file loss is confirmed; it does not diagnose Defender load.
⚠ Warning: Install it on a drive different from the one where your data was lost to prevent overwriting.
For a truly deleted local file, stop unnecessary writes to the original volume. Prepare a healthy separate destination and do not install recovery software on the source partition. Check whether a verified external backup already holds a safe copy. A disk that clicks, disconnects, or reports serious read errors needs an image or professional service, not repeated direct scans. Files moved into quarantine require a security review rather than a data-recovery workaround. Investigate the detection first.
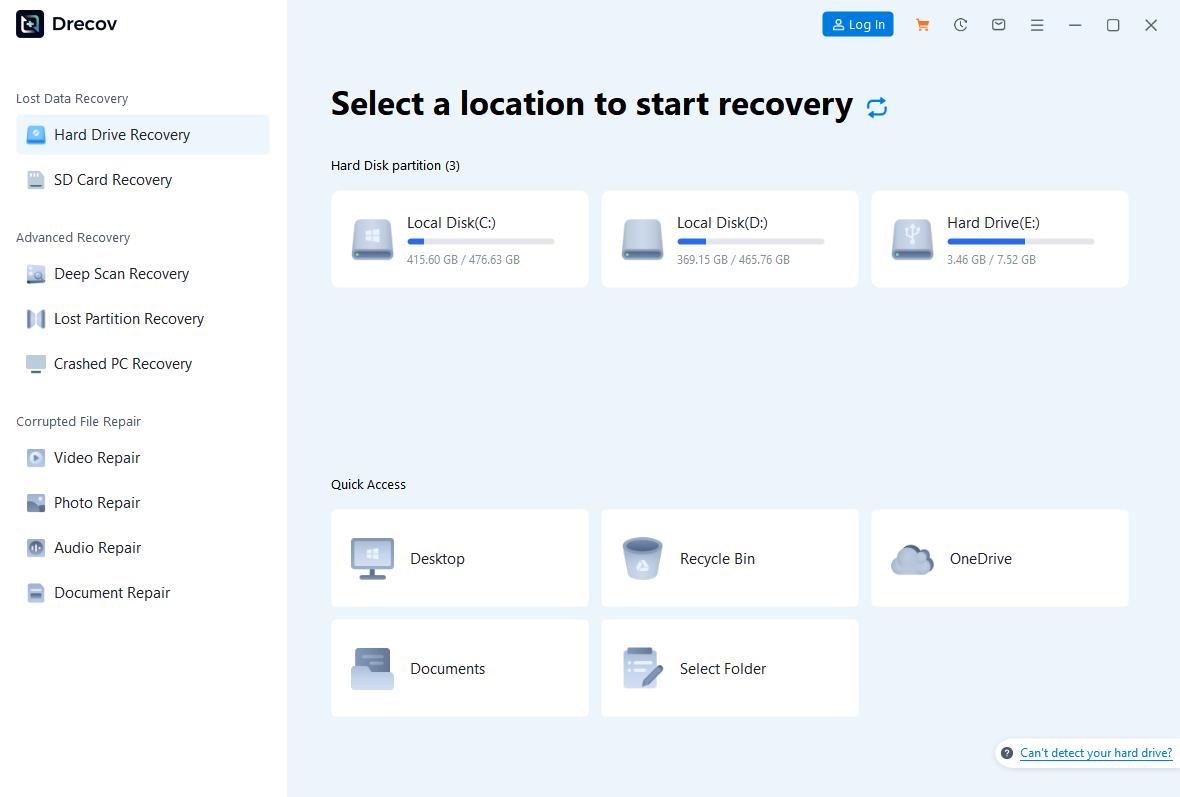
Step 1: select the former local file location
Launch Drecov on a working Windows system. Choose the stable volume that held the missing document before it disappeared. Confirm the device and path; do not scan every disk just because Defender used CPU. A file from Documents on the internal SSD calls for that original volume, whereas a missing item from a USB stick calls for the stable stick.
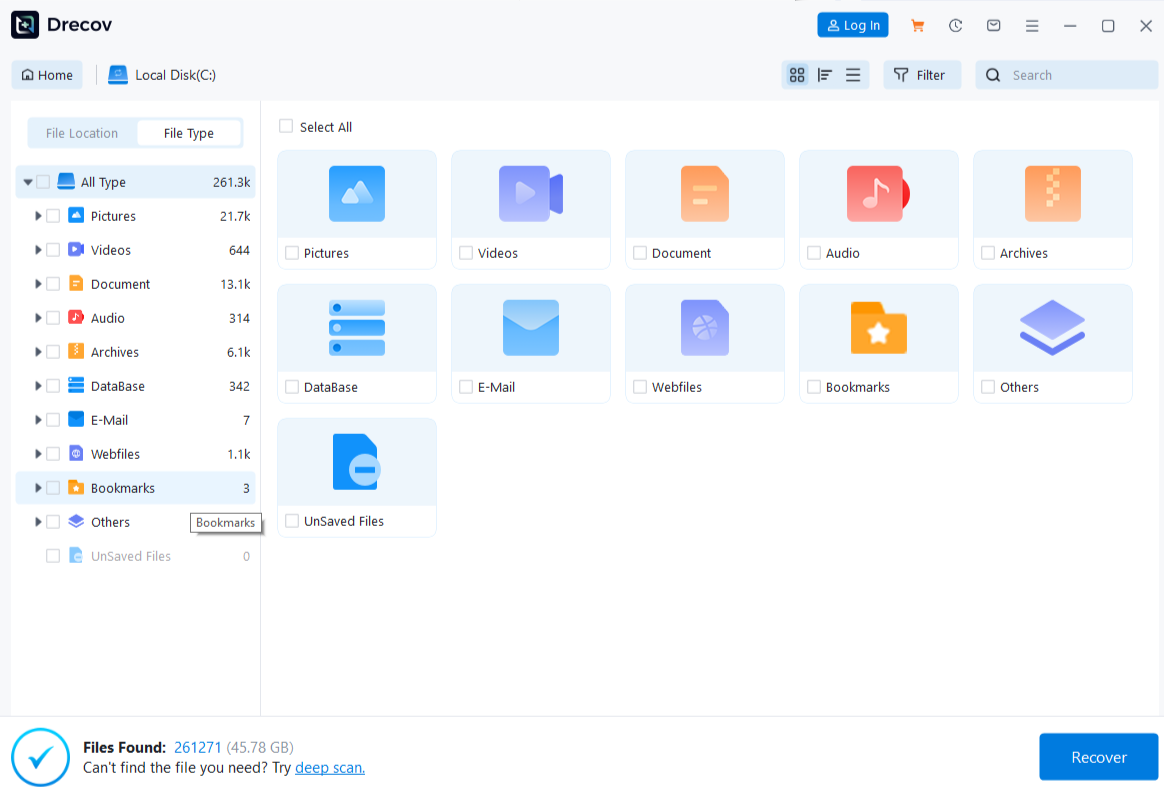
Step 2: scan, then narrow the candidates
Run Quick Scan first. If the needed file is absent and the device remains reliable, run Deep Scan. Use available filename, path, and type filters. Preview representative supported candidates, remembering that a preview does not guarantee every page or embedded object is intact. Stop direct scanning if hardware access deteriorates.
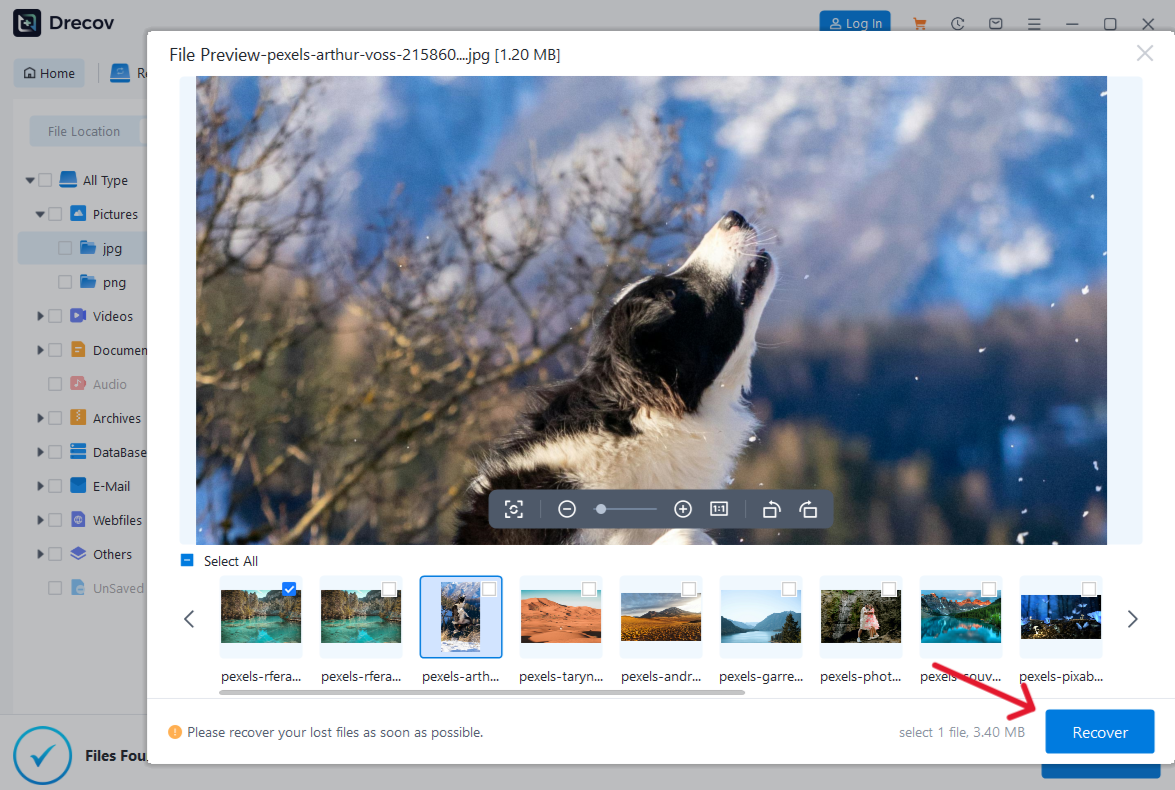
Step 3: restore elsewhere and check the result
Recover selected files to the prepared healthy destination, never to the source. If you do not see the output in the expected folder, check Drecov Folder or Recovery Folder there. Open a sample and verify the contents before copying anything back or changing security settings. Do not restore a file you suspect is malicious into normal use without an independent safety assessment.
⚠ Warning: Install it on a drive different from the one where your data was lost to prevent overwriting.
Check whether the fix worked
Repeat the workload that originally caused the spike while watching Task Manager. Compare CPU use over a similar period, not just one moment. A shorter burst that ends after the scan may be acceptable. If the same sustained load persists, record what still triggers it and review the official performance guidance or ask IT. Revert any exclusion that did not help. Keep a note of changes so the next person can understand the machine’s protection state.
Also verify that Windows Security still reports active protection and current definitions. A quiet CPU graph achieved by accidentally disabling security is not a successful fix. Try opening normal work files and ensure the device remains stable. If a storage error accompanies the slowdown, address that separately after securing data. Performance troubleshooting should not turn into a risky disk-repair session without evidence.
For a home PC, a small log is enough: date, task, peak duration, and result after each change. You need not become a security engineer. The practical question is whether you can work normally while the machine remains protected. If you cannot, a technician can use the recorded trigger to investigate more efficiently than a generic “Defender is slow” report.
Conclusion
Antimalware Service Executable high CPU is often a temporary scan, but sustained or repeatable load deserves a closer look. Identify the trigger, check Windows Security and updates, and make only narrow, justified changes. Do not disable protection to hide the symptom. Drecov has a separate role: when a local file really went missing from a stable source, it can scan that original location, help preview likely matches, and restore selected data to another healthy drive. It neither lowers Defender’s CPU use nor replaces a malware-safety decision.
⚠ Warning: Install it on a drive different from the one where your data was lost to prevent overwriting.